Docker × IDOM
Docker x IDOM, hardened images cut high-severity CVEs by 80% after a cyberattack
80% reduction in high-severity CVEs over two months
Post-cyberattack exposure to standardized, hardened foundation
Why it works
The cyberattack trigger gives the before-state genuine stakes, making the security outcome feel earned rather than routine. The piece earns its Resilience tag because the win is closing an exposure, not growing a number. The 50% image-size reduction and deployment speed gains add an Efficiency secondary thread, but the security hardening frames the whole story.
Steal this
The numbered implementation steps (update Dockerfiles, replace shell health checks, establish policy, document onboarding) show exactly how the migration was done, turning a vague 'we standardized' claim into a replicable playbook.
Members read free
See the full case study
Enter your email to see the full-page screenshot of this case study, and every other one in the library. One email unlocks all of them.
Free. No spam. Unsubscribe anytime.
You're in. Enjoy the library.
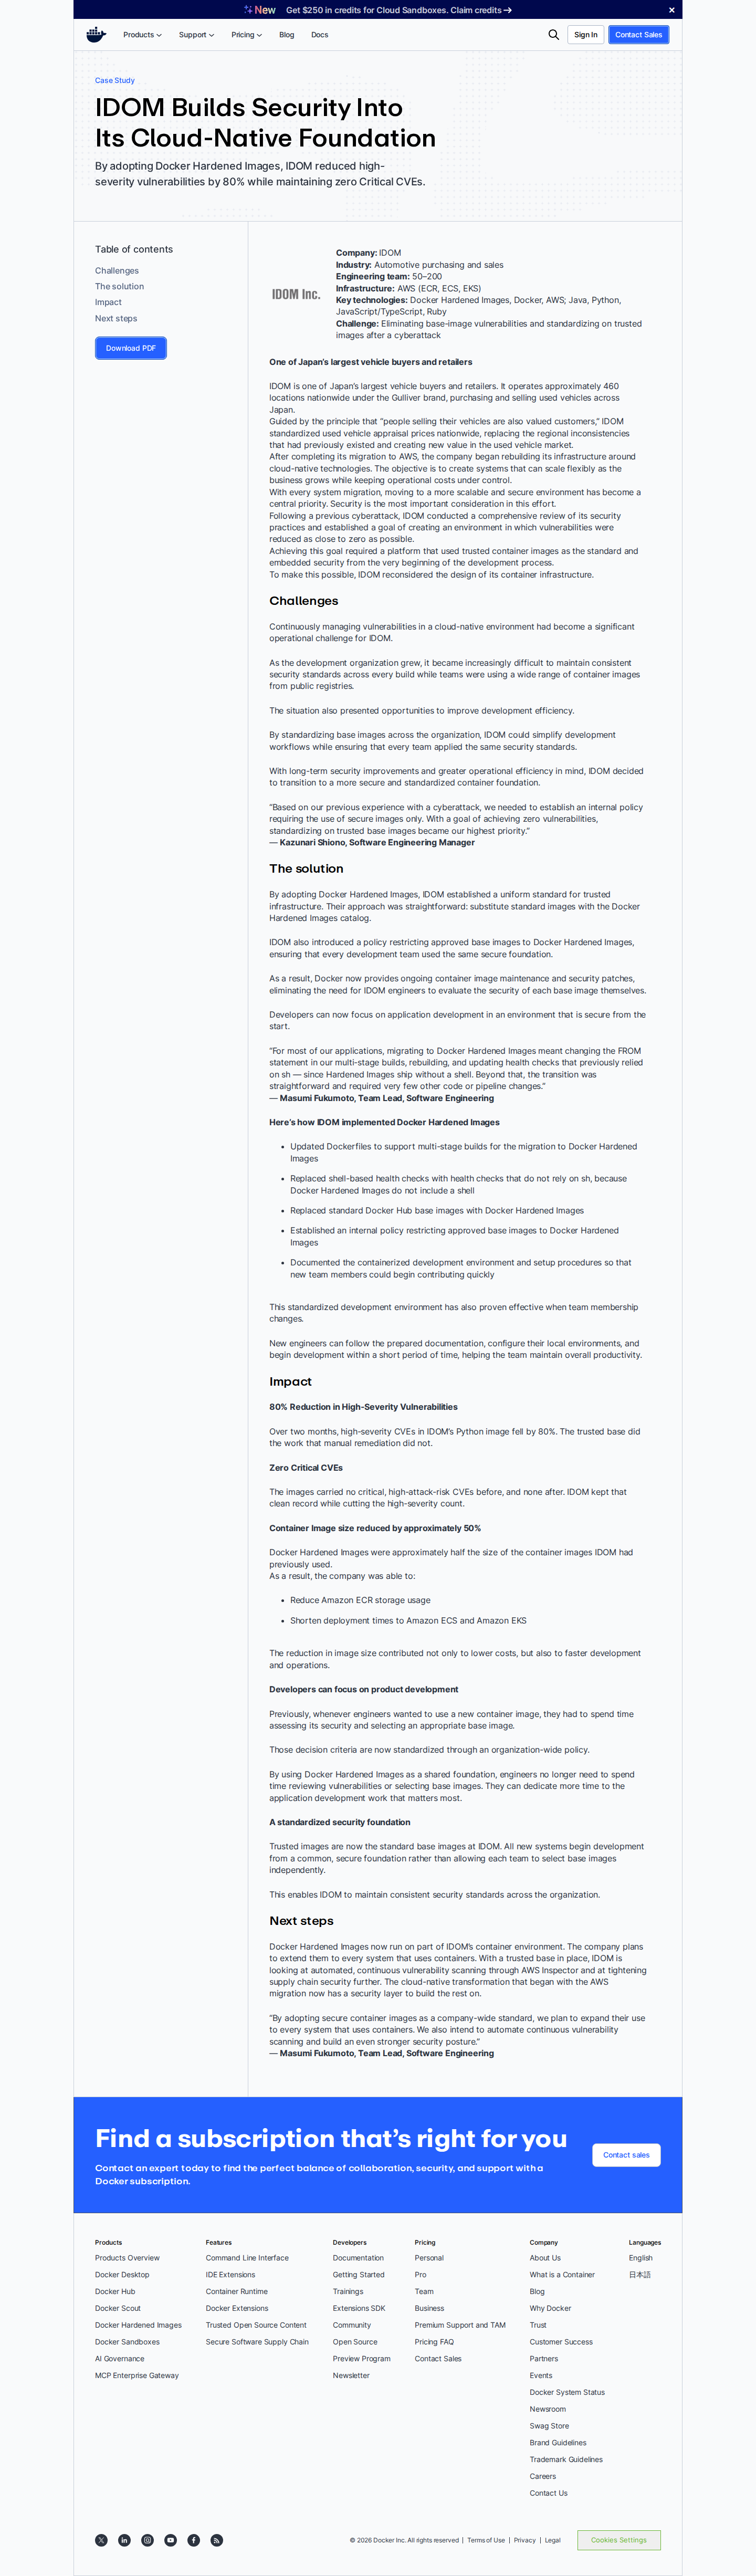 Click to enlarge ↗
This is editorial commentary and curation. The case study, screenshot, and all metrics are Docker's published work; we link to the source and lead with our analysis.