Snyk × Red Ventures
Snyk x Red Ventures: Container security at scale across 350+ AWS accounts
1,300+ new container images scanned daily across 350+ AWS accounts
Blind container security to actionable, automated visibility
Members read free
Unlock the full breakdown
Enter your email to open every case study in the library: the full screenshot, why it works, and the one thing worth stealing. One email unlocks all of them.
Free. No spam. Unsubscribe anytime.
You're in — enjoy the library.
Why it works
The case study earns its New Capability tag because Red Ventures had no working container scanning before, only broken home-grown tooling, so this is genuinely net-new rather than faster. The mechanism is described in enough detail to be instructive: CodeBuild pulls images, Snyk CLI inspects them, a custom discovery service auto-enrolls new images, and only fixable issues generate JIRA tickets. The story is thin on hard security outcome numbers beyond scale figures, which limits its punch.
Steal this
Filter findings before they hit the developer's workflow: only create tickets for issues that have a remediation available, so engineers see signal, not noise.
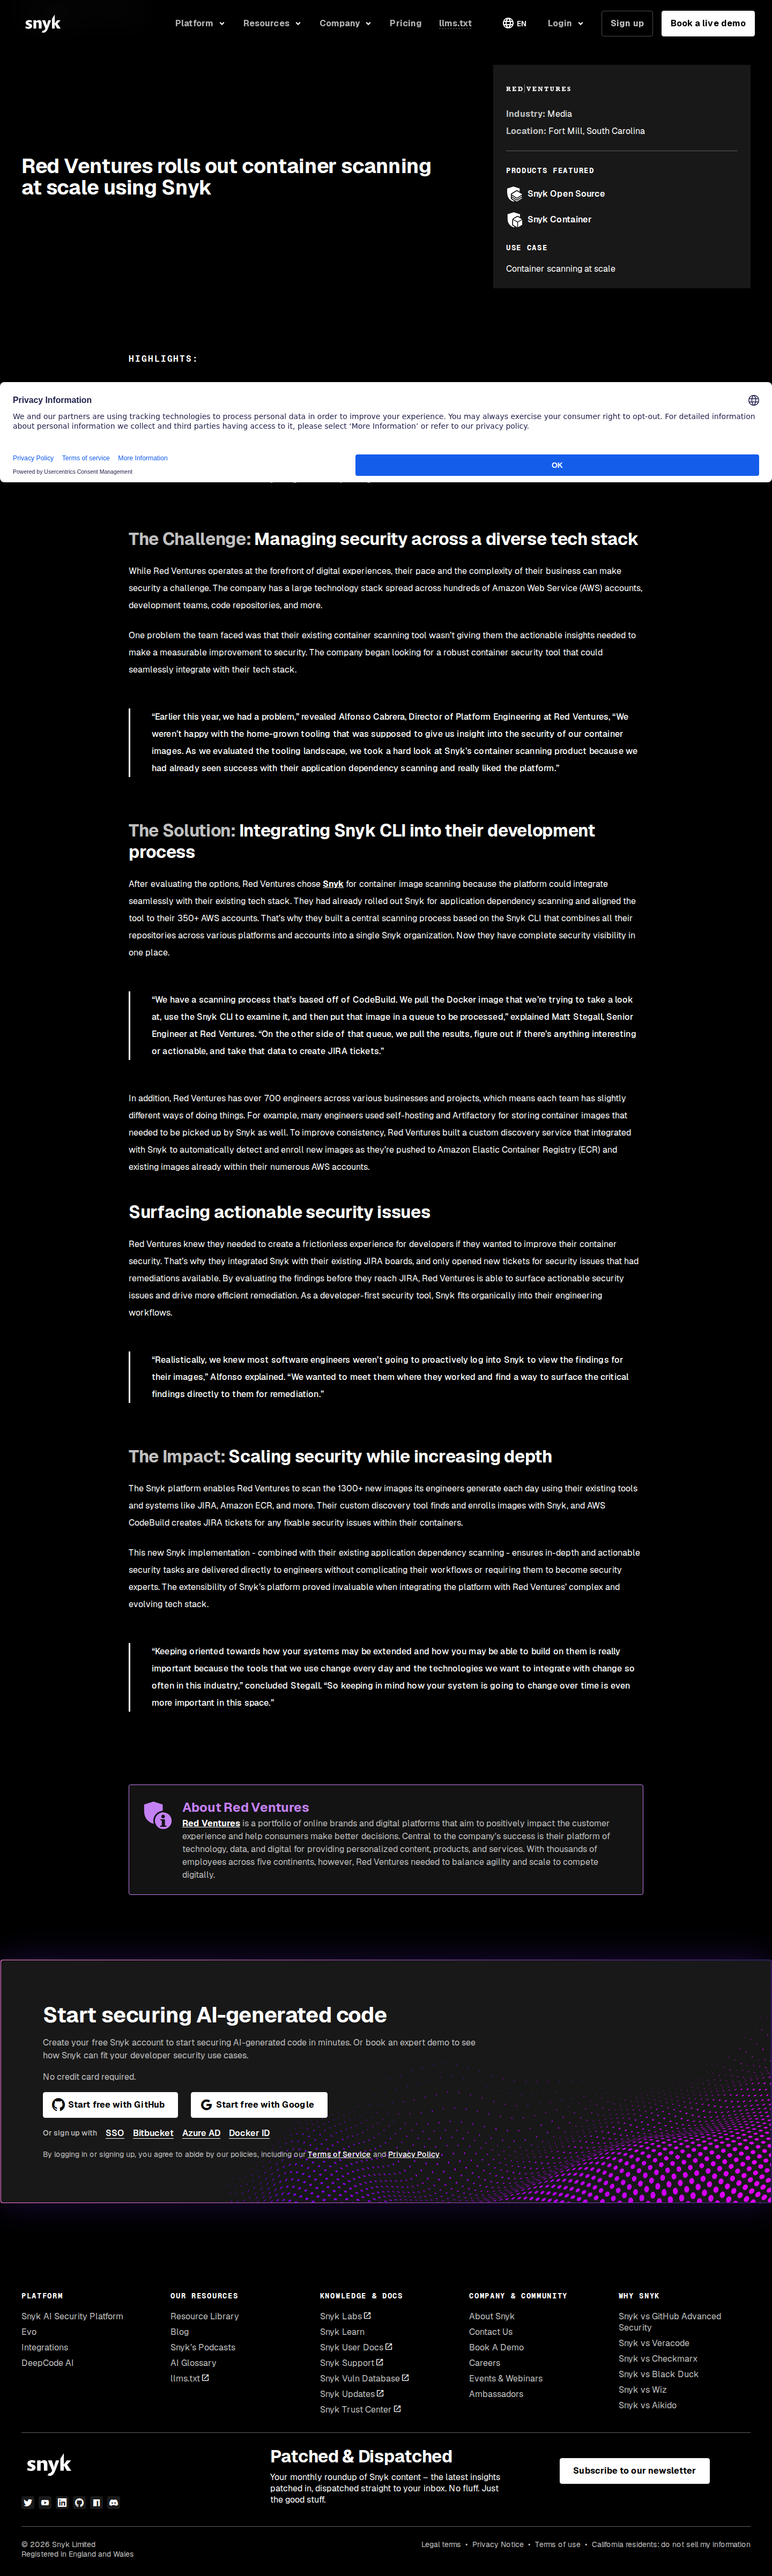 Click to enlarge ↗
This is editorial commentary and curation. The case study, screenshot, and all metrics are Snyk's published work; we link to the source and lead with our analysis.