Snyk × TechnologyOne
Snyk x TechnologyOne, from 90-minute rebuild loops to seconds
90 minutes to seconds to fix a vulnerability
Security as blocker to security as enabler
Why it works
The case study grounds its headline claim in a concrete mechanism: late-stage security feedback forced multi-hour rebuild cycles, and moving feedback into the IDE and PR scanning broke that cycle. The 90-minutes-to-seconds framing is specific and credible because the rebuild cost is explained step by step. The secondary angle, coverage across new languages and frameworks, is a genuine New Capability story that sits cleanly alongside the efficiency win without muddying it.
Steal this
Quantify the rebuild tax, not just the fix time. Saying 'a 30-minute build done three times equals 90 minutes of waste' makes the before-state viscerally expensive and makes the seconds-level improvement feel proportionate rather than oversold.
Members read free
See the full case study
Enter your email to see the full-page screenshot of this case study, and every other one in the library. One email unlocks all of them.
Free. No spam. Unsubscribe anytime.
You're in. Enjoy the library.
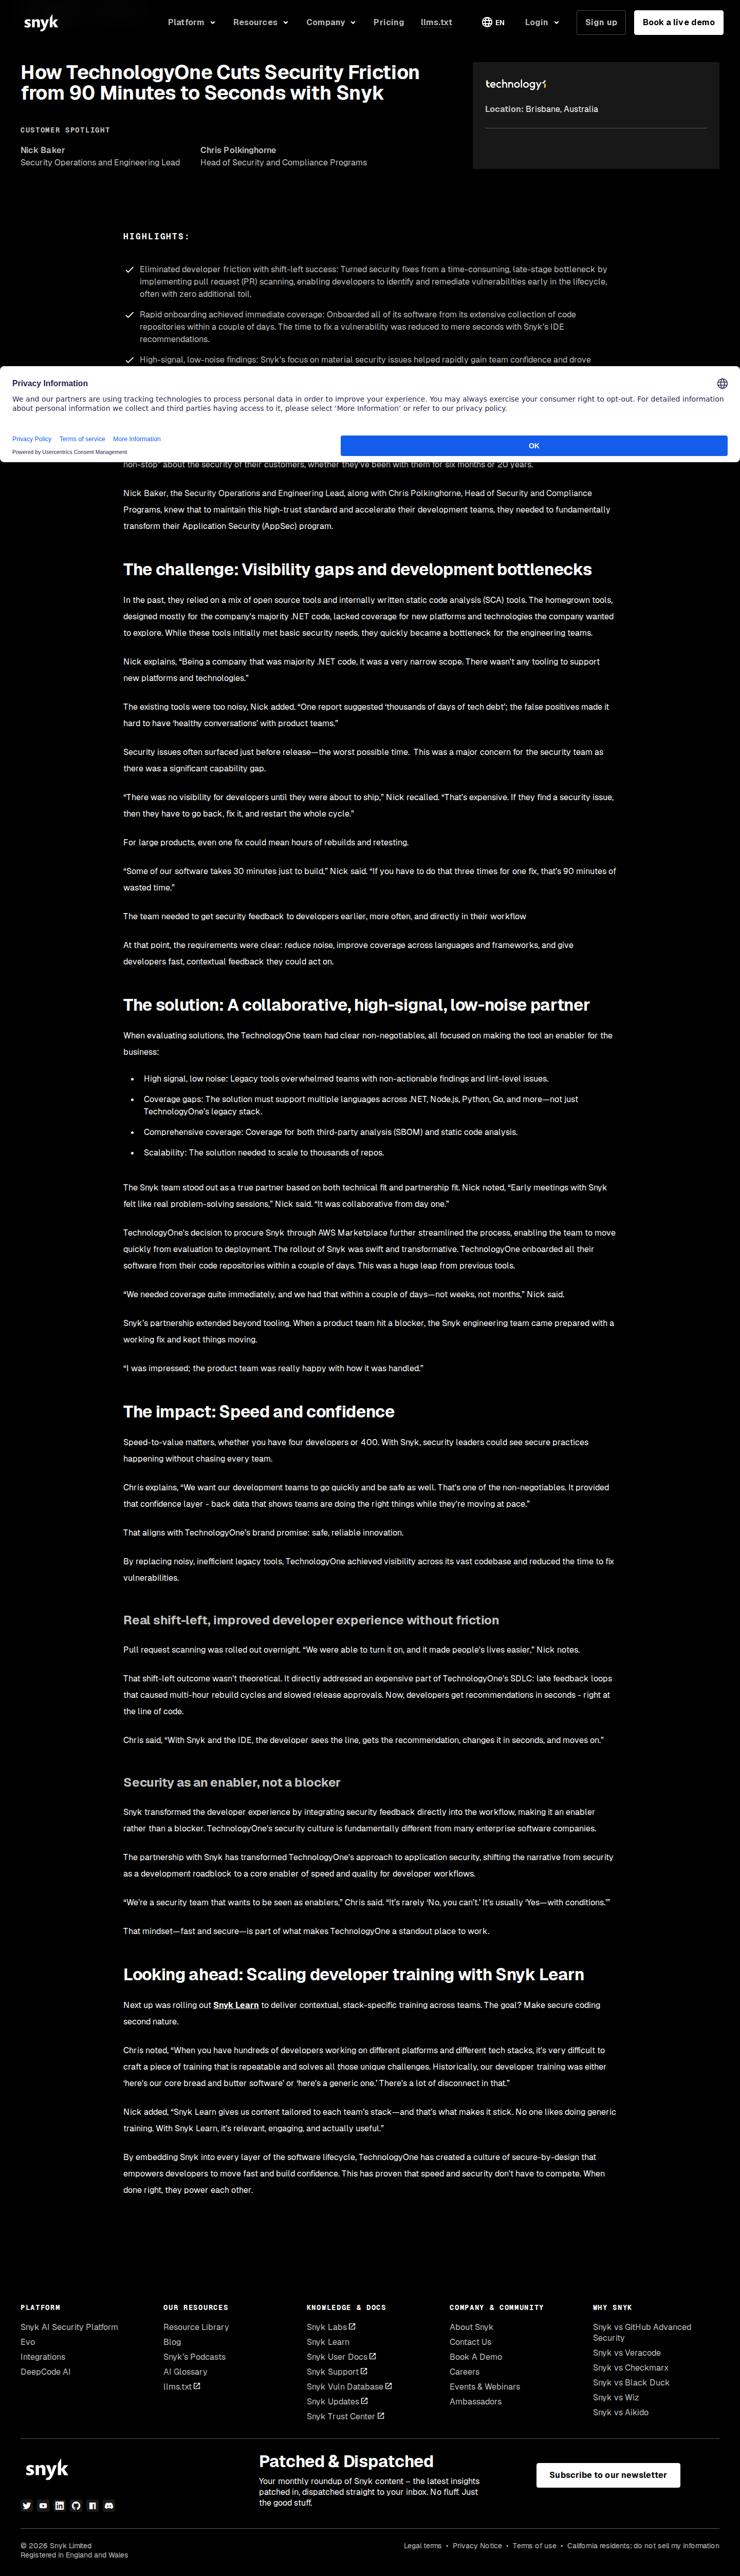 Click to enlarge ↗
This is editorial commentary and curation. The case study, screenshot, and all metrics are Snyk's published work; we link to the source and lead with our analysis.